Essential Eight Maturity Level 2 – What It Actually Means

What is Essential Eight Maturity Level 2?

Essential Eight Maturity Level 2 (ML2) represents a structured baseline for mitigating common cyber threats within Australian organisations, particularly those exposed to regulated environments.

ML2 requires implemented, enforced, and repeatable controls — not policy intent alone.
ML2 Is About Control Effectiveness

At ML2, organisations are expected to demonstrate:

  • MFA applied consistently across relevant users
  • Administrative privileges tightly controlled
  • Patch cycles managed within defined timeframes
  • Secure configuration standards implemented
  • Logging aligned to monitoring processes

Maturity implies operational consistency.

ML1 vs MLS2 vs ML3

The main differences between ML2 vs ML1 vs ML3:

  • ML1 — Basic control implementation
  • ML2 — Repeatable and consistently enforced controls
  • ML3 — Advanced resilience against sophisticated threats

For many Defence-aligned SMEs, ML2 forms the minimum commercial baseline.

Why ML2 Is Often Underestimated

Common misconceptions:

  • “We have MFA, so we’re compliant.”
  • “Our IT provider handles patching.”
  • “Logging is enabled by default.”

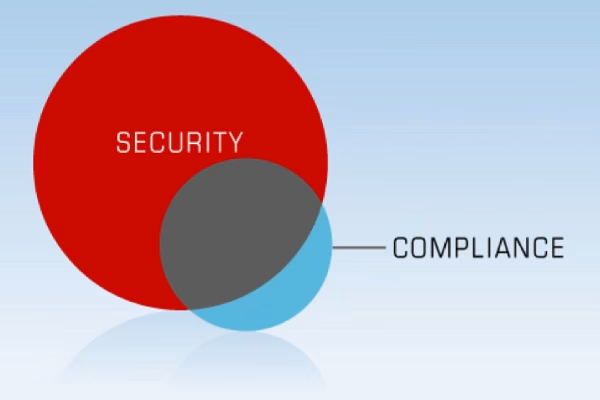
ML2 requires documented governance and evidence traceability — not just technical configuration.

ML2 Within a Defence Context

Where ML2 is connected to Defence procurement or DISP, expectations may extend beyond technical configuration into governance and documentation maturity.

For structured DISP support, see our
DISP Readiness page.

Unsure where you stand? Book a Strategy Call.

Book a Strategy Call